Driving Excellence
Quality and
Sustainability
We are commited to
Quality & Sustainability
At r2p Group, quality and sustainability are more than just goals—they are the principles that guide our business every day. We invite you to learn more about our approach and join us in our mission to create a sustainable future.
Why Quality Matters to Us
Our Environmental Responsibility
CRA / CVD Process
Vulnerability Handling and Disclosure Process
r2p is committed to the security of our products and services. We believe that coordinated vulnerability disclosure benefits our customers and the broader digital community.
This policy describes how security researchers and the public can report potential security vulnerabilities in r2p products and the commitments we make in response.
Scope
This policy applies to vulnerabilities in all software products developed and supplied by r2p GmbH and its subsidiaries.
Vulnerabilities in third-party components incorporated into or affecting the security of an r2p product are within the scope of this policy and may be reported to us.
Products that are no longer within their defined support period may fall outside the scope of this policy. However, we encourage the reporting of security vulnerabilities affecting any r2p product, including unsupported products.
Vulnerabilities solely affecting third-party products or services are outside the scope of this policy.
Rules for Security Reach
The following testing activities are not permitted under this policy:
- Destructive testing or intentional modification or deletion of data.
- Installation of malware, backdoors or other mechanisms intended to maintain persistent access.
- Accessing, copying or exfiltrating data beyond the minimum necessary to demonstrate the vulnerability.
- Denial-of-service (DoS/DDoS) attacks or other testing that may impair the availability or stability of systems or services.
- Social engineering, including phishing, impersonation and other attempts to obtain information through deception.
How to Report a Vulnerability
To report a security vulnerability, contact our security team:
- E-mail: productSIRT@r2p.com
- Portal: staging.r2p.com
Reports containing sensitive information should be encrypted using our published PGP key (see below). Do not report security vulnerabilities through public issue trackers, social media or support tickets.
We accept reports in English, German and Danish.
Information to Include
To help us investigate and assess the vulnerability, please include as much of the following information as possible:
- Affected product, software version and relevant configuration (if known).
- A clear description of the vulnerability, including its potential security impact.
- Steps to reproduce the vulnerability and, where appropriate, a proof of concept, screenshots, logs or other supporting information.
- Any indication that the vulnerability is being actively exploited, if known.
- The date and time the vulnerability was discovered, if known.
- Your contact details (optional).
Reports may be submitted anonymously. However, providing contact information enables us to request additional information and provide status updates.
What Happens After You Report
When a vulnerability is reported to r2p, the following steps are taken:
- Acknowledgement: We will acknowledge receipt of the report within 3 business days.
- Initial assessment: Within 7 business days, we will review and assess the vulnerability.
- Communication: If you have provided contact information, we will keep you informed of material progress and may contact you for additional information.
- Remediation: Confirmed vulnerabilities are addressed based on their severity, exploitability and potential impact. We aim to remediate vulnerabilities without undue delay and will coordinate an appropriate disclosure timeline with the reporter where applicable.
- Notification: Where appropriate, we will notify affected users when a vulnerability has been remediated or when mitigations or security updates are available. We will also notify the reporter, provided contact information has been supplied.
If available, preliminary versions of software fixes may be provided to the reporter for verification.
Coordinated Disclosure
r2p is committed to coordinated vulnerability disclosure (CVD). We ask reporters not to publicly disclose vulnerability details before the agreed disclosure date and to coordinate any planned publication with r2p.
We will work with the reporter in good faith to coordinate an appropriate disclosure timeline. The timeline will take into account the severity and potential impact of the vulnerability, the risk to users, evidence of active exploitation, and the availability of mitigations or security updates.
If a vulnerability presents an immediate or significant risk to users or is known to be actively exploited, r2p may accelerate remediation, mitigation and disclosure activities as appropriate.
Following remediation or the availability of appropriate mitigations, r2p may publish information about the vulnerability to help affected users understand the risk and take appropriate action. Publication may be limited where necessary for security, legal, contractual or privacy reasons.
PGP Key File
Fingerprint 02B7 9A42 FA6E D399 3A39 A2E9 4946 B3F4 60B4 B5D2
Download PGP Key File
r2p GmbH
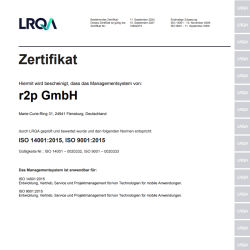
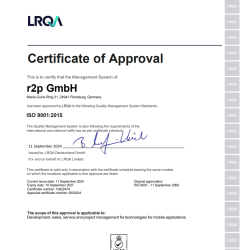
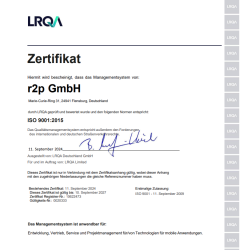
ISO 9001 & ISO 14001 (EN)
ISO 9001 & ISO 14001 (DE)
KBA Certificate (EN)
KBA Certificate (DE)
commitment to quality excellence
ISO certified
To ensure we meet these high standards, r2p Group has implemented a robust Quality & Environmental Management System. This system is rigorously maintained and certified according to the globally recognized ISO 9001:2015 and ISO 14001:2015 standards. These certifications reflect our ongoing commitment to quality excellence and our proactive approach to environmental stewardship.
r2p UK Systems LTD
ISO 27001
ISO 9001
ISO 14001
Cyber Essentials Plus
CHAS Certificate